
Hacks & BuildsSamsungsmart TVmitmproxyeMudhraRust
A developer used a compromised eMudhra certificate authority key to replace the ads on his Samsung TV home screen with family photos
Daniel Vrátil's Rust server only works because his 2022 TV still trusts keys that eMudhra revoked on October 18, so the photos stay up as long as he never updates it.
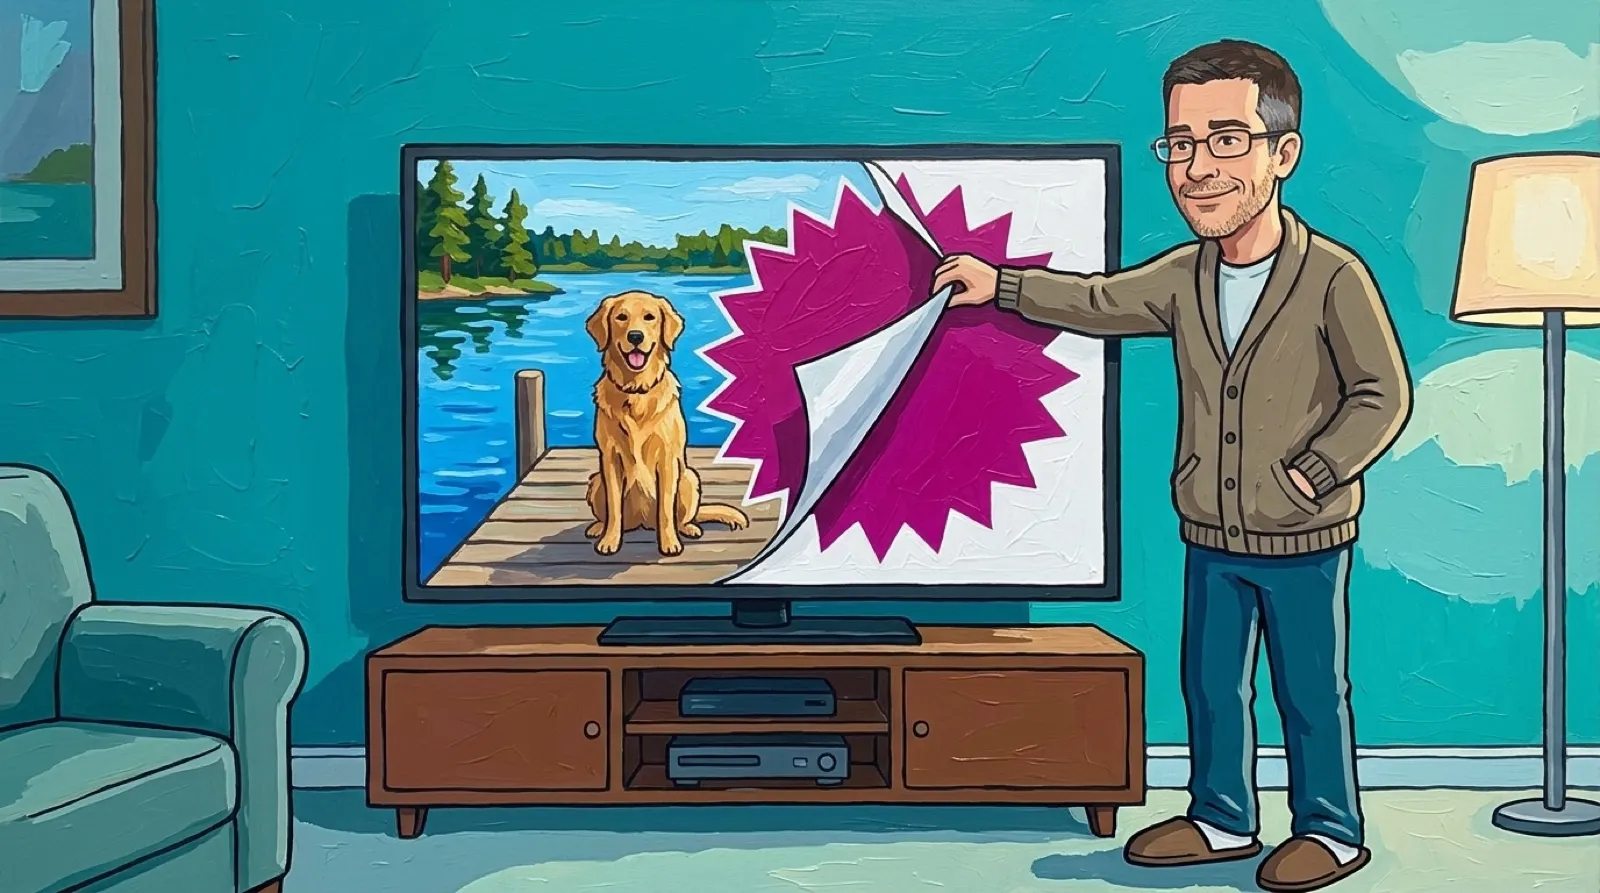
Daniel Vrátil’s 2022 Samsung TV used to show him ads on its home screen. Now it shows him his family. He swapped one for the other with a certificate that was never supposed to be usable, and with a server written in Rust.
His starting point was irritation. He wrote that he thinks it is “absolutely disgusting that a device that I paid for and own” serves ads. He had been blocking them with Pi-hole until a change to his homelab network broke that setup, so he went looking for something sturdier than a blocklist.
The sturdy option meant watching the TV’s own traffic. A Mikrotik router sends the TV’s connections to a Raspberry Pi running mitmproxy in transparent mode, and iptables on the Pi redirects ports 80 and 443 to it. That showed him the TV calling catalyst.adgrx.com when certain events happen. When he returns to the Smart Hub, it asks tvx.adgrx.com/impressions/tile for an ad and gets back either an empty JSON object or an ad.
The snag was encryption. Normally mitmproxy works because a device trusts its custom certificate, and he wrote that “unfortunately, some devices don’t allow adding custom SSL certificates to their truststore - like my Samsung TV.” That was the end of the usual road.
What opened a new one was the failure of a certificate authority. He wrote that “around the same time, the eMudhra CA certificate fiasco took place.” eMudhra’s own statement says eight intermediate CAs “were revoked because their published keys were weak,” and that it revoked all eight on October 18. The Register reported that researcher Scott Helme found one of the private keys “is the number 4,” and wrote: “I recovered all of them from their public certificates on my laptop just now.”
A key that is the number 4 can be signed with by anyone who can count. His TV still trusted the eMudhra certificates, so a certificate signed with that key looked legitimate to it, and mitmproxy could read the traffic.
Reading was only step one. He wrote “a simple server in Rust that handles the same /impressions/tile endpoint and always returns JSON with an ad,” and the ad links to a random photo of his family. Everything else under *.adgrx.com gets a 204 No Content, which also quiets the tracking. He generated a wildcard certificate for *.adgrx.com, signed it with the compromised CA, and pointed those domains at his NAS through his router’s DNS. A small web frontend lets him manage the images.
The code is in danvratil/samsung-tv-adspoofer on GitHub, described there as a way to “show custom photos and pictures in your Samsung TV SmartHub instead of adverts!” He has tested exactly one set: “I only have single Samsung TV I can test this on: QE65Q60B - Q60B (2022) series.” Patches for other models are welcome.
He is clear about the catch. “Obviously, this will only work as long as my TV trusts the compromised eMudhra certificates,” he wrote. That ends when the certificate expires or when Samsung revokes the trust through an update. For now he blocks updates, which he notes has risks of its own.
The photos stay up only as long as the TV never gets patched.
The ad slot on a TV Vrátil paid for now belongs to him, and it got that way through the system meant to keep outsiders from doing exactly this. Whether any other TV is open to it depends on which certificate authorities it still trusts, and that list is the maker’s to change.
The same stale trust that makes his hack work is the thing an update would fix, which is why he holds updates back. A TV that trusts a key nobody should trust will believe whoever holds it. Today that is a man with a NAS and a photo album, and eMudhra’s own statement says the keys it revoked were published.
The only ad on his TV that nobody skips.