Securityciscopasswordspentestingincentives
A pharmacy chain's firewall admin password was 'password,' and IT fought the rating because a high finding killed their bonuses
Red-teamer Dahvid Schloss decoded a Cisco type 7 enable password on a big US pharmacy chain's edge firewall. The hour-long shouting match that followed was really about who got paid.
Schloss, now COO of the red-team shop Suzu Labs, wasn’t hired to break in. The job was a plain audit of the chain’s switches, routers and firewalls, and the client asked not to be named.
“So, I come across this firewall,” Schloss said. “That is an edge firewall, meaning this is what touches the internet.” Its enable password, which is Cisco’s word for the admin login, was “password. Just p-a-s-s-w-o-r-d.”
He didn’t guess it. He read it straight out of the config. “That enable password was stored as Cisco IOS type 7, which isn’t really a hash,” he said. “It’s more of a reversible encoding with a publicly known key.”
Cisco has said as much in its own IOS hardening guide for years: the encoding behind it “is a simple Vigenère cipher,” and “Type 7 passwords are not a secure form of password storage.” A centuries-old pencil-and-paper cipher was guarding the admin door of a pharmacy network.
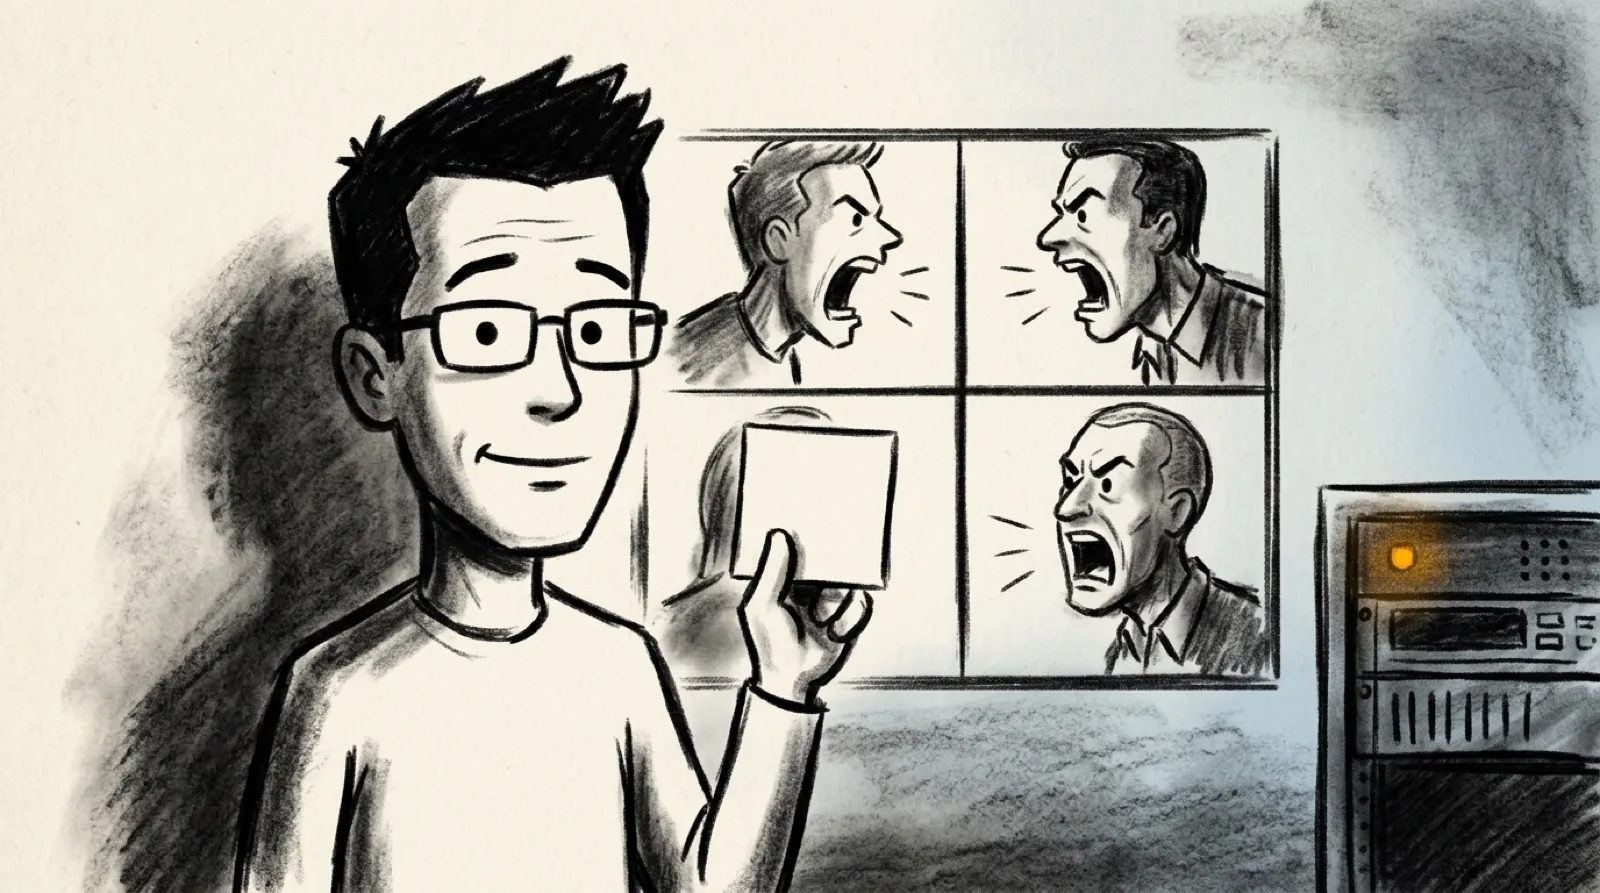
Schloss marked it a high finding. The auditors, who had commissioned the work, put him on a call with their team, the whole IT team and his own manager. Then the two sides screamed at each other for more than an hour while the red team stared into their webcams.
“It’s like ‘Why? Who’s gonna? What does it matter? No, this isn’t a high-priority find. This is maybe a medium,’” is how Schloss described the IT side’s pushback.
He never got to finish presenting. Later he learned why the fight ran so hot: the audit department controlled IT’s bonuses, and any high finding eliminated them. The client kept asking him to walk through that one finding again for the next three years, long after he’d moved on. Whether the password ever changed, the story doesn’t say.
Security scorecards tied to pay are going to keep producing this exact meeting. When the number on the report decides the bonus, people negotiate the number, and the finding with the most money on it gets the most lawyering. Expect more audit contracts to separate “who rates the risk” from “who gets paid on it,” and expect red-teamers to start asking, before the engagement, who’s compensated on their findings.
The open question is the one Schloss couldn’t answer either: after three years of re-explaining, did anyone ever log into that firewall and type a new password?